​​​​Sovereign Identitiy Access management to secure all your applications​​

Reduce reliance on passwords, strengthen single sign-on across your applications and give users an easier way to access the tools they use every day.

​​​​Sovereign Identitiy Access management

The challenge

Without identity access management, authentication varies from one application to another

More applications mean more login credentials to manage.
Teams rely on an ever-growing number of applications to do their jobs. Without single sign-on (SSO), each new application can mean another username and password to remember, reuse, reset or lose.

MFA protects some applications, but not all

When multi-factor authentication (MFA) is deployed application by application, some resources may require additional verification while others remain protected by a password alone.

This inconsistency creates gaps in an organisation’s authentication security.
applications selection

In hybrid environments, authentication is difficult to unify

Cloud applications, on-premises systems, and different identity sources do not always speak the same language. Without an identity layer connecting users and applications, organisations end up managing separate authentication mechanisms across their environment.

our identity provider is business-critical, but do you really control it?

Centralising authentication makes the identity provider one of an organisation’s most critical systems. Yet many organisations have little say over where their identity data is hosted, who can access it or which regulations apply to it.

The solution

Sovereign Identity Access, a sovereign ​MFA and ​SSO ​solution for your employees

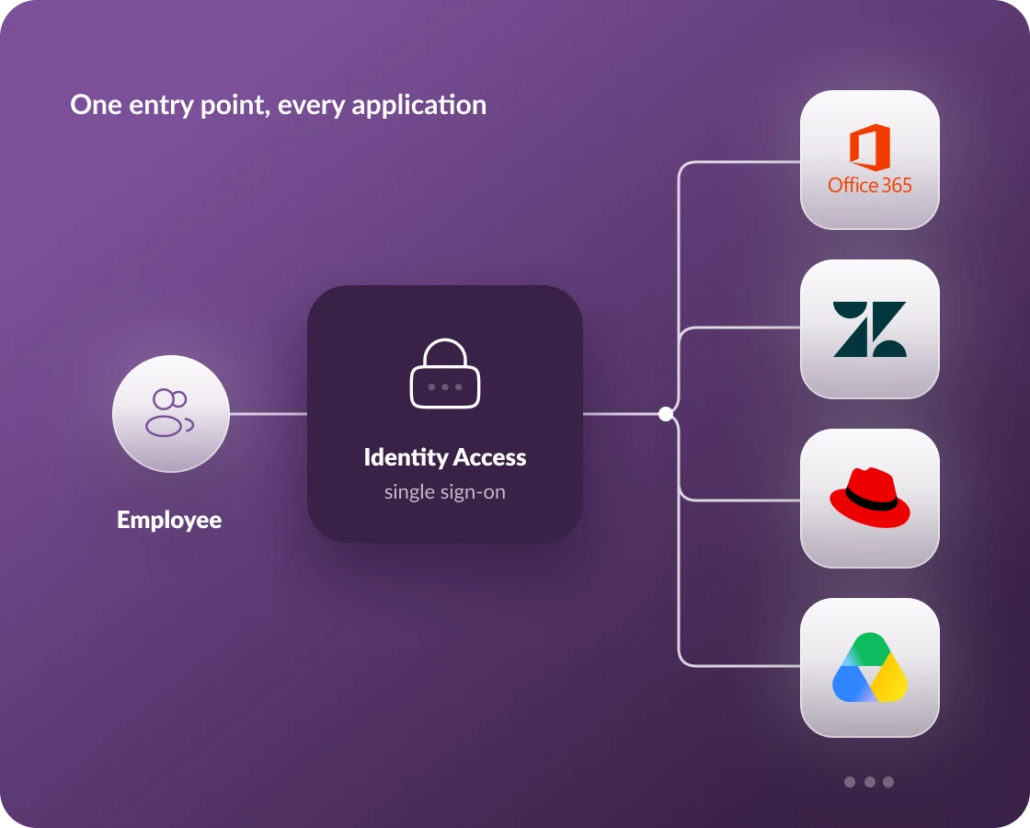
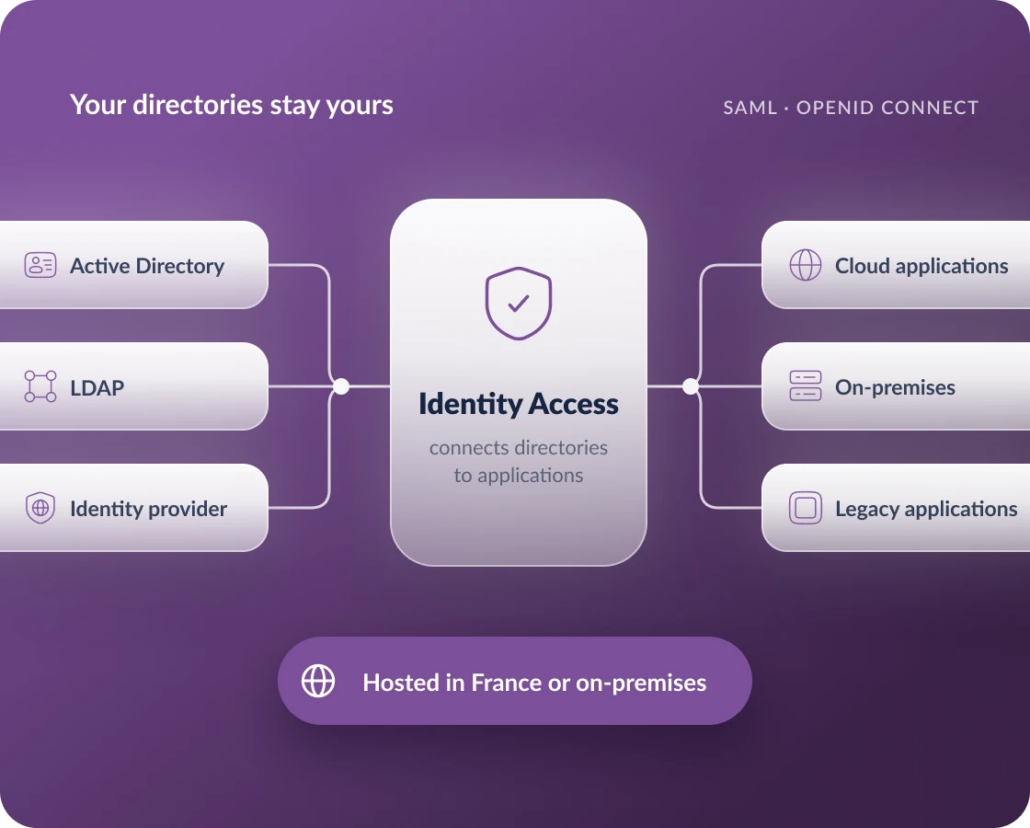
Sovereign Identity Access is an authentication and federation layer that centralizes the way employees authenticate with applications. Our SSO solution combines SSO, MFA, and identity federation to provide a consistent access experience across the entire organization, whether hosted in France or deployed on-premises.

Single Sign-On

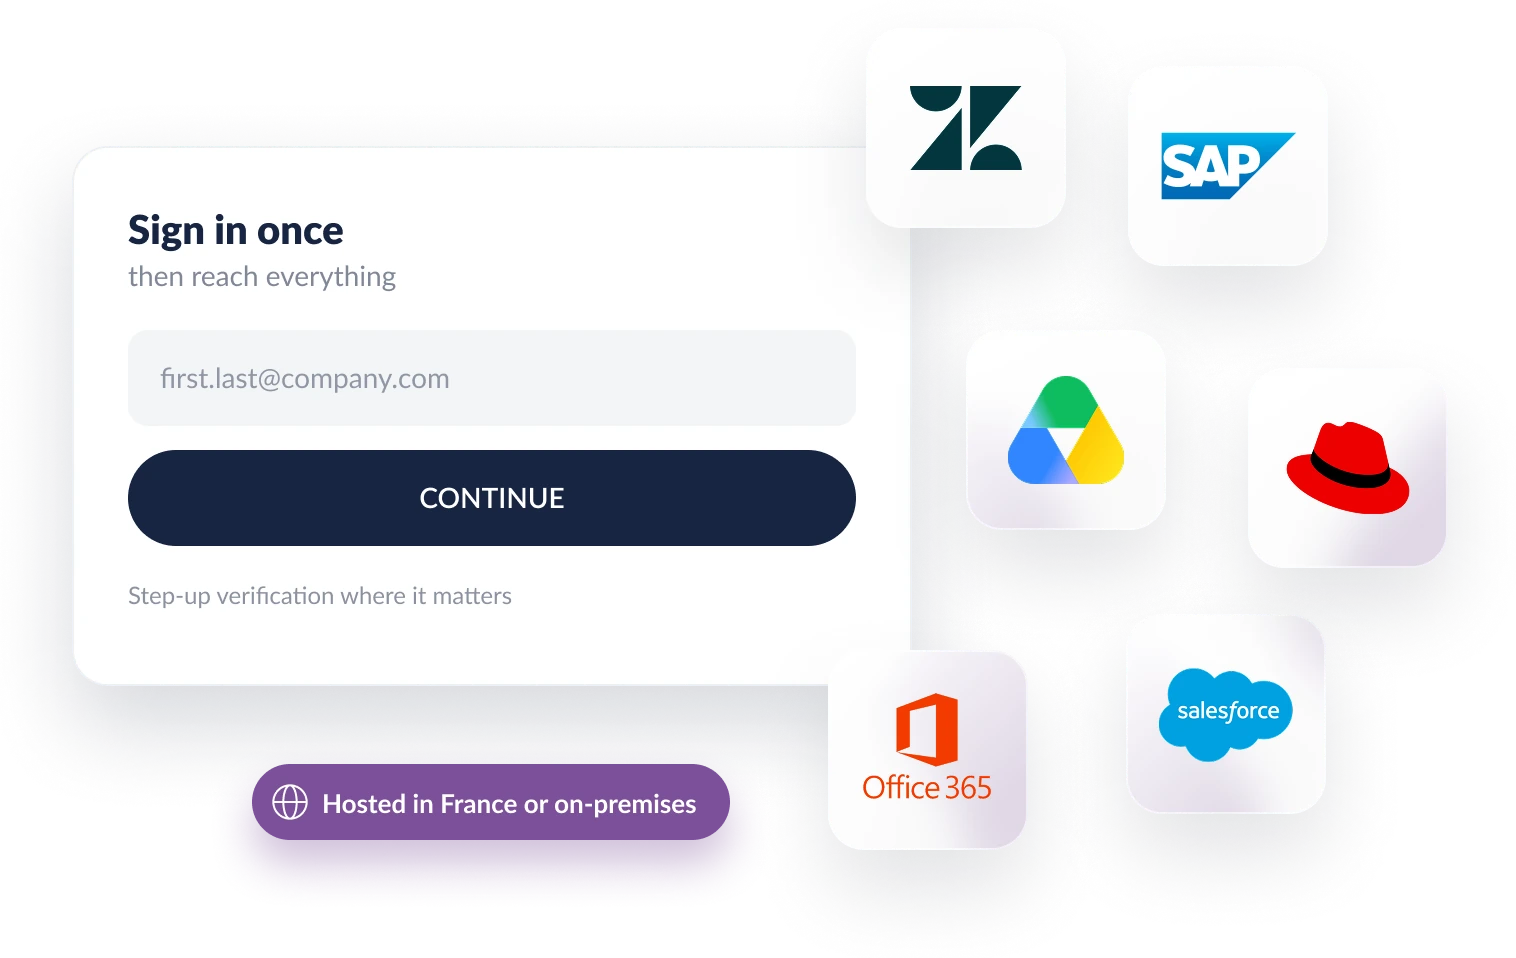
Give employees a single, secure entry point to the applications they use every day.

With single sign-on (SSO), users authenticate once and move between connected applications without having to enter different credentials each time.
Fewer logins mean less password fatigue, fewer interruptions and a smoother employee experience.

Single Sign-On

Multi-Factor Authentication

Renforcez l'authentification grâce à des options MFA flexibles, adaptées à chaque profil d'utilisateur, à chaque application et à chaque exigence de sécurité.

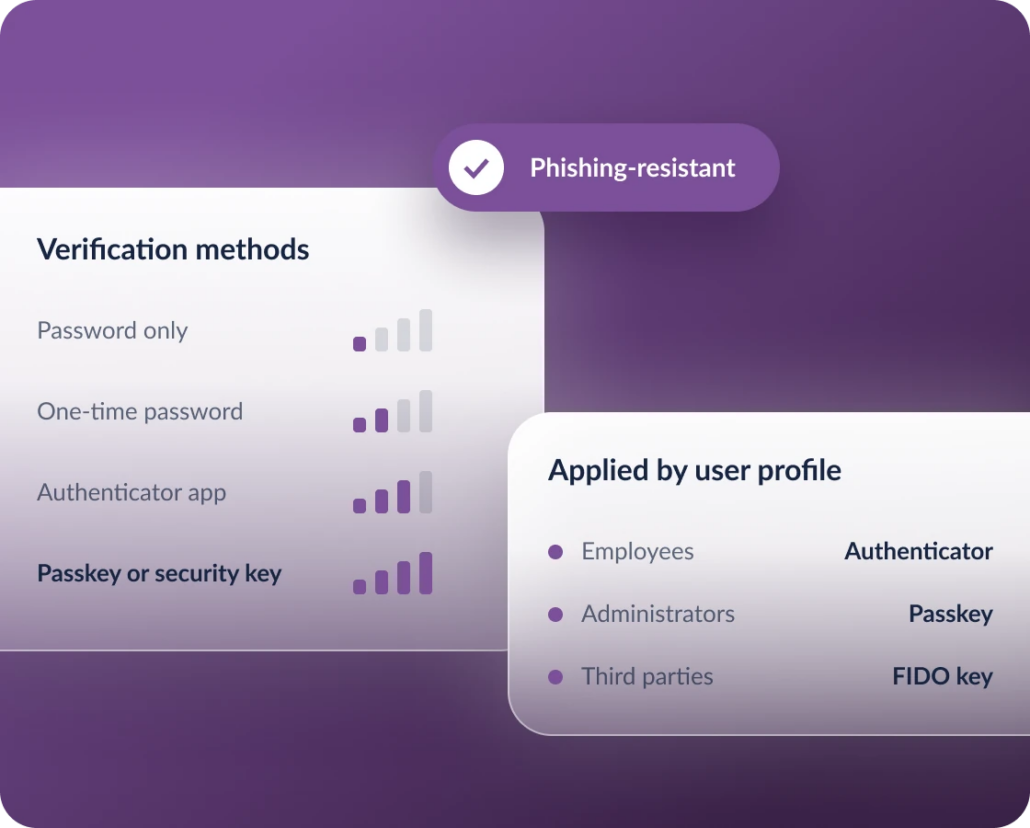
Strengthen authentication with flexible MFA options tailored to each user profile, application and security requirement.
Support a wide range of verification methods, from authenticator apps and one-time passwords to phishing-resistant authentication, while giving organisations the flexibility to increase protection where it matters most.

Multi Factor Authentication

Identity Federation

Extend secure access across your applications and environments without replacing the identity infrastructure you already trust.

WALLIX Sovereign Identity Access works with your existing identity providers and directories. It connects cloud, on-premises and legacy environments using standards such as SAML and OpenID Connect.

Federation identites

Benefits

Why adopt a sovereign identity access solution for your organisation?

Reduce the number of passwords users need to manage

Every additional password introduces another risk of credential reuse, compromise or loss. SSO reduces repeated authentication across connected applications: employees can work more easily, and the organisation relies less on separate passwords for each service.

Apply strong authentication across all your applications

Sovereign Identity Access gives organisations a central authentication layer from which stronger verification (MFA) can be applied across connected applications, providing a more consistent security controls. Users benefit from a familiar authentication experience, while security teams strengthen protection for application access.

Simplify access without compromising security

Security measures work best when users can actually use them.
SSO reduces repetitive logins, while MFA strengthens verification where it matters. Employees spend less time authenticating and more time using the tools they need.
The result: stronger identity security without making access more complicated.

Stay in control of your identity layer

Your authentication layer contains sensitive data about your users’ identities and the resources they access. Whether deployed in the cloud or on-premises, Sovereign Identity Access keeps this data under European governance and within your control.

Watch WALLIX Sovereign Identity Access in action

Découvrez comment notre solution SSO, la MFA et la fédération d'identité se combinent pour simplifier l'accès et renforcer l'authentification dans l'ensemble de votre environnement applicatif.

FAQS

Frequently asked questions about MFA, SSO, solution and Identity Federation

What is an SSO solution, and what does Identity Access do?

Identity Access is an authentication and federation layer for your employees. It brings together single sign-on (SSO), multi-factor authentication (MFA) and identity federation: employees benefit from a single, consistent way to sign in, while security teams have a central point from which to manage the protection of those logins.

Do we need to replace our existing identity provider or directory?

No. WALLIX Sovereign Identity Access is designed to work with the identity infrastructure you already trust, not replace it. Wherever possible, it verifies credentials directly against your own directory rather than storing a separate copy.

Which MFA methods do you support?

A wide range of options, from authenticator apps and one-time passwords to phishing-resistant authentication using passkeys. Security teams can apply stronger verification where it matters most rather than treating every application in the same way.

What does “phishing-resistant” actually mean?

After entering their password, users confirm their identity with a passkey (fingerprint, facial recognition or PIN) or a security key. This verification is tied to your organisation’s official sign-in page: even a convincing fake page cannot capture anything reusable. It is a more robust second step, not a way to eliminate the password.

Where is our identity data hosted, and what do you store?

Identity Access is hosted in France. It is designed to store only the information needed to authenticate a user and to share with each connected application only the data it requires. For organisations that need to keep identity data entirely within their own infrastructure, on-premises deployment is also available.